iFrame for eCommerce and Online Payments
Secure Credit Card Collection and Tokenization Without Redirecting Customers
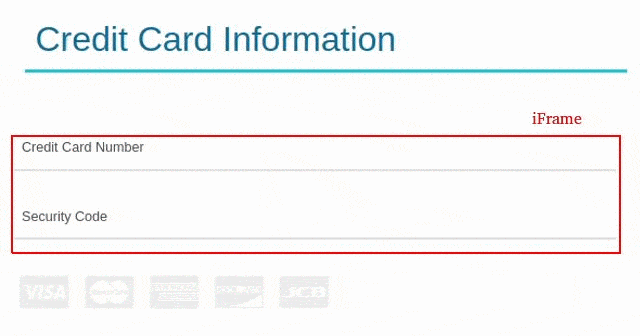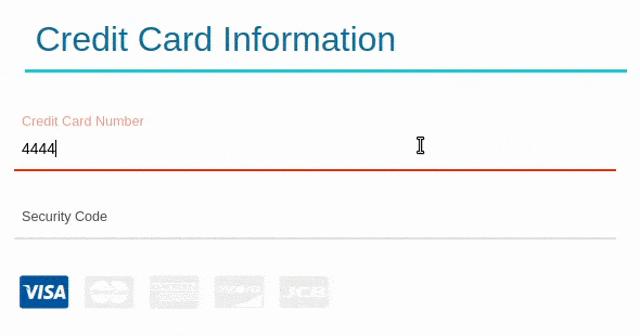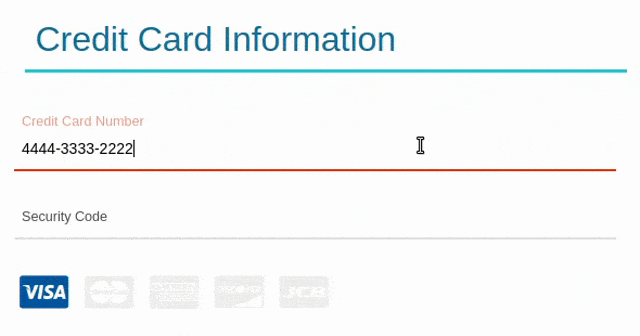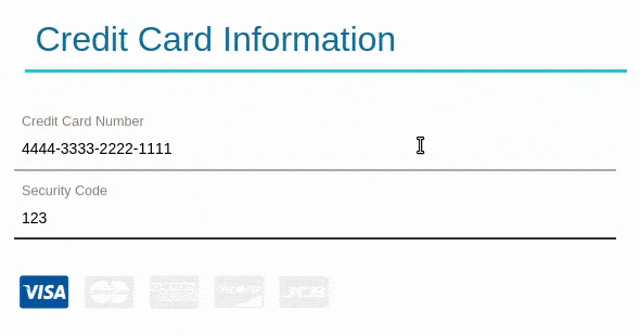
HostedPCI’s secure payment iFrame allows businesses to collect credit card information directly within their websites, applications, and eCommerce checkout pages without requiring customers to navigate to a separate payment website.
By embedding HostedPCI’s secure payment fields into your existing checkout experience, you can collect and tokenize sensitive cardholder data without passing raw card numbers through your application servers.
Built on HostedPCI’s PCI DSS Level 1 payment infrastructure, our eCommerce iFrame solution supports secure payment collection, credit card tokenization, and integration with multiple payment gateways.
Whether you operate an eCommerce website, SaaS platform, subscription service, or enterprise payment application, HostedPCI helps you maintain control over your checkout experience while reducing direct exposure to cardholder data.
Types of iFrames
- iFrame V6 (ACH) – Latest Version
- iFrame V5
- iFrame V4
- Interactive iFrame (V2)
- Basic iFrame with CVV (V1)
- Credit Card PAN only iFrame
- CVV only iFrame
How Does the HostedPCI Payment iFrame Work?
HostedPCI’s payment iFrame embeds secure payment fields directly into your existing checkout page. Customers enter their card information within the HostedPCI-hosted fields, while your business maintains control over the surrounding checkout design and customer experience.
The integration uses HostedPCI’s JavaScript-based iFrame components alongside your existing payment form.
A Simple, Secure Payment Collection Process
1. Integrate the Payment iFrame
Embed HostedPCI’s secure card collection fields into your existing checkout page or application using the provided integration components and configuration instructions.
2. Collect Payment Information Securely
Customers enter their credit card details into HostedPCI-hosted fields without leaving your website. Sensitive cardholder information is transmitted to HostedPCI rather than passing through your application servers.
3. Tokenize Cardholder Data
HostedPCI securely captures the payment credentials and returns a token representing the collected card information. Your application can use this token without storing the original card number.
4. Process Payments Through Your Gateway
Use the token with HostedPCI’s payment APIs to initiate transactions through your configured payment gateway.
This process allows your business to maintain its existing checkout experience while separating sensitive card collection from its application environment.
View iFrame Integration Documentation
Key Features of HostedPCI’s Secure Payment iFrame
PCI DSS Scope Reduction
HostedPCI’s payment iFrame helps reduce exposure to cardholder data by collecting sensitive payment information through secure, HostedPCI-hosted fields rather than merchant application servers.
Seamless eCommerce Integration
Embed secure payment fields within your existing website, checkout page, or application. Customers remain on your website while completing their payment information.
Customizable Payment Fields
Configure the appearance and behaviour of your secure payment fields to align with your checkout experience.
Supported options include card number formatting, masking, field highlighting, and card type identification.
Secure Credit Card Tokenization
Replace sensitive card information with secure HostedPCI tokens that can be referenced within supported payment workflows without storing raw card numbers in your application.
Multiple Payment Gateway Support
HostedPCI supports integrations with multiple payment gateways, helping businesses maintain flexibility in their payment processing infrastructure without relying on a single gateway’s hosted checkout interface.
Credit Card and ACH Collection
HostedPCI offers iFrame configurations for collecting both card information and ACH payment details, depending on the integration and processing requirements.
Built for Secure and Flexible Payment Workflows
PCI DSS Level 1 Payment Infrastructure
HostedPCI provides secure payment collection and tokenization services through its PCI DSS Level 1 infrastructure.
Businesses can integrate HostedPCI’s secure payment fields into their websites as part of a broader payment security and compliance strategy.
Support for Different Payment Applications
HostedPCI’s payment iFrame can support a range of payment collection requirements, including online purchases, customer payment portals, subscription services, and card-on-file workflows.
With tokenization and multiple payment gateway integrations, businesses can build payment experiences around their operational requirements without handling raw card numbers directly in their application servers.
Payment iFrame vs. Hosted Payment Page: What’s the Difference?
Both payment iFrames and hosted payment pages allow businesses to outsource the collection of sensitive payment information. The primary difference is how customers interact with the payment experience.
Hosted Payment Page
With a hosted payment page, customers are typically redirected to a separate payment provider website to enter their payment details.
Payment iFrame
With a payment iFrame, secure payment fields are embedded directly within your website or application. Customers enter their payment information without leaving your checkout page.
HostedPCI’s payment iFrame allows businesses to maintain their existing checkout design while using third-party infrastructure to securely collect sensitive cardholder data.
For organizations that want secure payment collection without redirecting customers, an embedded payment iFrame can provide a more integrated checkout experience.
Secure Payment Collection for Different Industries
eCommerce Websites
Collect credit card payments securely through your existing online checkout without redirecting customers to another website.
SaaS and Subscription Platforms
Integrate secure card collection into customer portals, subscription management applications, and recurring billing workflows.
Enterprise Payment Applications
Support custom payment workflows requiring secure payment collection, cardholder data tokenization, and integration with multiple payment gateways.
Travel and Booking Platforms
Securely collect and tokenize payment credentials during booking and reservation workflows, with tokens available for later charges such as deposits, balances, or incidentals, subject to supported payment arrangements.
Customer Payment Portals
Allow customers to securely enter or update stored payment information within authenticated portals without requiring your application to handle raw card numbers.
PCI DSS Compliance and Payment Page Security
Businesses that accept card payments must meet applicable PCI DSS requirements, even when payment information is collected through a third-party provider.
HostedPCI’s secure payment iFrame helps reduce the amount of sensitive cardholder data handled by merchant systems. However, outsourcing card collection does not automatically eliminate PCI DSS responsibilities.
Protecting Your Checkout Page From Script Attacks
Under PCI DSS v4.x, the security of the website containing an embedded payment iFrame remains an important consideration.
Even when cardholder information is collected within secure, third-party-hosted fields, malicious scripts running on the surrounding checkout page can introduce risks.
For example, a compromised script could display fraudulent payment fields over the legitimate iFrame and trick customers into entering their card details directly into an attacker-controlled form.
The PCI DSS v4.0.1 SAQ A eligibility criteria address this risk by requiring applicable eCommerce merchants using embedded payment forms to confirm that their websites are protected against script-based attacks that could affect their eCommerce systems.
PCI SSC guidance describes different ways to demonstrate this protection, including techniques associated with PCI DSS Requirements 6.4.3 and 11.6.1 or qualifying confirmation from the compliant payment service provider.
Using HostedPCI’s payment iFrame does not automatically establish SAQ A eligibility. The appropriate compliance requirements depend on your complete implementation, payment environment, and the criteria applicable to your business.
Businesses should review their payment-page security controls and confirm their compliance requirements with their assessor, acquirer, or applicable payment brand.
Frequently Asked Questions
What is a payment iframe?
A payment iframe is an embedded HTML frame that displays secure payment fields within a website or application. It allows customers to enter payment information directly into fields hosted by a payment service provider rather than through the merchant’s own application server.
Is the HostedPCI payment iFrame PCI compliant?
The iFrame runs on HostedPCI’s PCI DSS Level 1 validated infrastructure. Your own PCI DSS compliance still depends on how the solution is implemented within your website and payment environment.
Does the customer leave my website to complete a payment?
No. HostedPCI’s payment iFrame is embedded within your existing checkout page, allowing customers to enter payment information without being redirected to a separate website.
Does HostedPCI store credit card information?
Yes. HostedPCI provides secure cardholder data storage and tokenization services. Businesses can use tokens to reference securely stored payment credentials without retaining raw card numbers within their own applications.
Can I customize the appearance of the payment fields?
Yes. HostedPCI offers field styling and configuration options, including formatting, masking, field highlighting, and card type identification.
Can I use HostedPCI with my existing payment gateway?
HostedPCI supports integrations with multiple payment gateways, allowing businesses to retain their preferred payment processing relationships.
See our Supported Payment Gateways page for available integrations.
Does HostedPCI support recurring payments?
Yes. HostedPCI’s tokenization infrastructure can support card-on-file and recurring payment workflows through supported gateway integrations, subject to applicable transaction and authorization requirements.
Does HostedPCI support ACH payments?
Yes. HostedPCI offers ACH-enabled iFrame configurations for collecting applicable bank account details. ACH processing availability depends on your payment gateway and integration configuration.
Does using a payment iFrame eliminate PCI compliance requirements?
No. A payment iFrame can help reduce PCI DSS scope by separating sensitive card collection from your application environment, but merchants still have responsibilities for securing their websites and payment workflows.
For example, merchant-controlled checkout pages may be vulnerable to malicious scripts that attempt to replace or overlay legitimate payment fields. Under the applicable PCI DSS v4.0.1 SAQ A eligibility criteria, merchants using embedded payment forms must address script-attack risks.
The appropriate SAQ and compliance obligations depend on your complete payment implementation.
Secure Your Online Payment Collection With HostedPCI
Integrate secure credit card collection into your existing website without redirecting customers or passing raw card numbers through your application servers.
HostedPCI’s payment iFrame combines embedded payment fields, secure tokenization, PCI DSS Level 1 infrastructure, and multiple payment gateway integrations to support modern eCommerce and enterprise payment workflows.
Whether you’re launching a new checkout experience or updating an existing payment application, our team can help you review the integration options and determine the right configuration for your business.
Case Studies
Travel
This merchant required the ability to collect and store credit cards securely from their booking page until required for payment. The transaction process starts with the first 2 requests being sent to the airline company to determine if tickets were available and then the 3rd transaction needs to be sent securely with the credit card number to the airline.
Municipality
This municipal merchant of ours required the ability to accept credit cards from their clients in a PCI compliant way in order to reduce their PCI scope as much as possible. The biggest trouble was to collect the customer’s card over the phone while being able to provide guidance to their clients regarding the transaction process and also collect the card during off hours with an unassisted IVR.